Ship with confidence.
Let the tests write themselves.
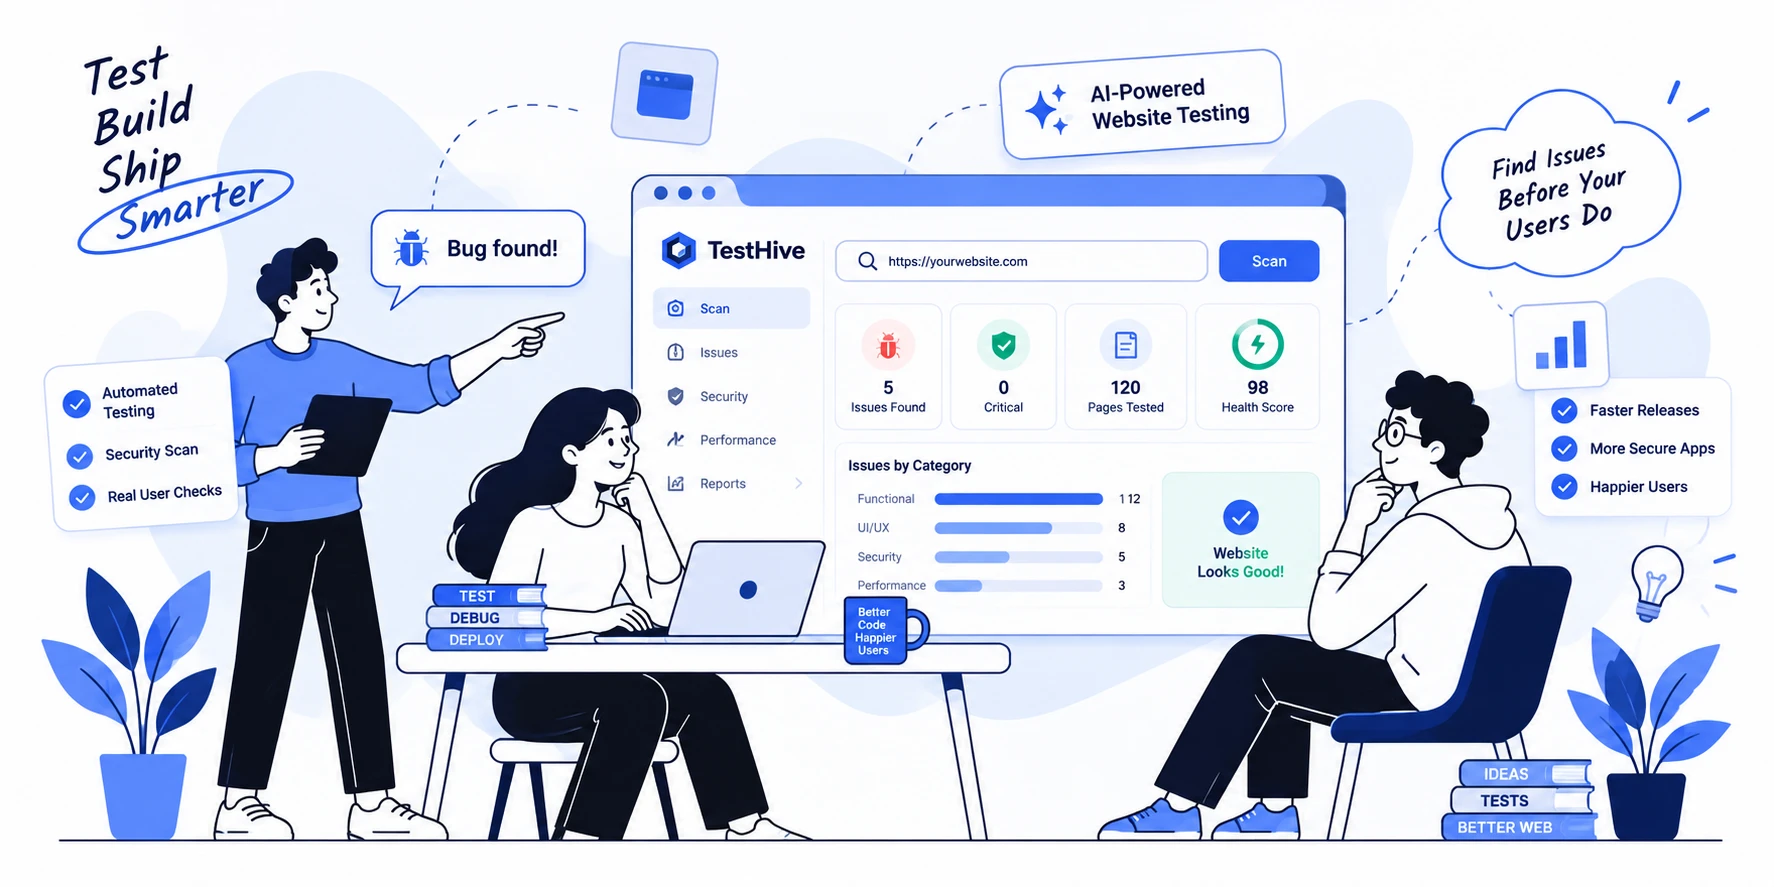
TestHive crawls your application, generates a full test suite, runs it in parallel browser workers, and tells you what actually broke — with the evidence to prove it.
5 free site audits a month · No credit card · Set up in two minutes
—
runs completed
—
pages tested
—
findings reported
—
Test runs completed
—
Pages tested
—
Findings reported
—
tests generated
Everything a QA team does, running on its own
Autonomous generation
From a URL to a full test suite
TestHive crawls your application, reverse-engineers the product intent, and writes executable tests for every route, form and input it finds. No framework setup, no prompts, no hand-written locators.
- Discovers routes, forms and interactions automatically
- Role-based locators that survive markup changes
- Signs in with test credentials to reach the pages behind login
Diagnosis that refuses to guess
Real bug, or a brittle test?
Every failure is classified as a product bug, test fragility or an environment problem before anything else happens. Healing only ever touches fragile tests — assertions, auth flows and pages showing errors are off-limits, so a real regression can never be quietly patched away.
- Three-way classification on every failure
- Heals are live-validated against your running app
- Every heal is logged with the patch and the reason
Evidence, not opinions
See exactly what the browser saw
Each run keeps per-step screenshots, console output, network requests with bodies, and a execution trace for anything that failed. Runs are compared against the previous one so you know what newly broke, not just what is red.
- Regression detection against the last run
- Flaky tests scored and quarantined, never hidden
- Screenshots and traces for every failure
Zero-touch Quality Milestones
Reach 100% confidence on every deployment
Track QA progression across releases with unified metrics. From first URL crawl to regression verification, TestHive measures flakiness, coverage depth, and production stability so your team can deploy fearlessly.
- Milestone tracking across releases and environments
- Flakiness score calculation and quarantine alerts
- Unified requirement traceability from ticket to test run
From URL to a verified suite in three steps
- 1
Point it at your app
Paste a staging or production URL. Add test credentials if you want the pages behind login covered.
- 2
It plans, writes and runs
Routes are crawled, a test plan is generated, and the suite executes across isolated parallel browser workers.
- 3
Review what changed
Failures arrive classified and evidenced. Fragile tests heal themselves; real bugs are filed with a fix suggestion.
Simple, predictable plans
Every plan runs the full pipeline. You only choose how many sites you audit each month — one audit run is one credit.
Free
5 site audits / month
For individual builders getting started.
- 5 shared credits / month
- 1 organization member
- Frontend & backend testing
- CLI & MCP integration
- Community support
Pro
100 site audits / month
For power users needing high-frequency testing.
- 100 shared credits / month
- 1 organization member
- 5 parallel browser workers
- Auto-healing locator repair
- Custom configs & test schedules
Team
1000 site audits / month
Best for small teams collaborating on web apps.
- 1,000 shared credits / month
- Up to 5 organization members
- Shared organization credit pool
- 10 parallel browser workers
- Priority Slack & email support
Business
5000 site audits / month
For scaling companies with fast release cycles.
- 5,000 shared credits / month
- Up to 20 organization members
- 25 parallel browser workers
- REST & GraphQL API access
- Dedicated onboarding session
Enterprise
Unlimited site audits / month
Dedicated infrastructure, custom SLA and governance.
- Custom monthly credits
- Unlimited organization members
- Dedicated cluster & workers
- SSO, SAML & fine-grained RBAC
- SOC 2 Type II audit logs & VPC
Free QA and security tools
Audit performance, validate APIs, scan headers and check accessibility — no account needed.
Website Testing & Site Audit
Deep crawl and health check for broken links, SSL, performance and security headers.
Open toolAPI Testing & Security Tool
Run REST API tests with custom headers, payloads, status assertions and latency benchmarks.
Open toolSecurity Headers Scanner
Inspect CSP, HSTS, X-Frame-Options, Permissions-Policy and CORS for defence in depth.
Open toolWebsite Performance & Vitals
Measure TTFB, DNS lookup, DOM load latency and Core Web Vitals with concrete fixes.
Open toolAccessibility & Usability
Audit WCAG 2.1 compliance, contrast, missing ARIA and unlabelled form fields.
Open toolBroken Link Checker
Find internal 404s, redirect chains, invalid anchors and malformed URLs across your app.
Open toolXML Sitemap Validator
Validate syntax, detect broken routes in sitemap.xml, or generate a valid sitemap.
Open toolRobots.txt Analyzer
Test crawler access rules and user-agent directives; avoid accidental de-indexing.
Open toolTechnical SEO Analyzer
Evaluate Open Graph, canonicals, JSON-LD structured data and heading hierarchy.
Open toolCommon questions
What is API testing in software and how does TestHive automate it?
API testing validates endpoints directly — functionality, latency, boundary behaviour and security — without going through the UI. TestHive scans your API endpoints, verifies JSON schemas, tests authentication guards and benchmarks latency.
What is test automation and why does it matter?
Test automation runs repeatable test suites in CI/CD so regressions are caught before release. It removes the manual regression bottleneck and shortens release cycles.
QA automation vs manual testing — where does each fit?
Automation excels at repetitive regression, high-speed execution and continuous verification; manual testing suits subjective visual review and exploration. TestHive explores like a human tester and emits reproducible browser code.
What is agentic AI testing?
An agent inspects the live DOM, infers the product intent, generates positive and negative cases, executes them in a real browser, and repairs brittle locators when the UI changes — while refusing to mask genuine defects.
How does self-healing avoid hiding real bugs?
Healing only runs when a failure is classified as test drift. It never touches assertions, auth or payment flows, or pages showing an error, and every heal is live-validated and logged with its patch and reason.
Does it perform security testing?
Non-invasive checks: SSRF-safe target validation, Content-Security-Policy and CORS evaluation, header leak detection, and input injection probes that assert payloads are escaped rather than executed.
Stop chasing bugs by hand.
Point TestHive at your app and get a verified, self-maintaining test suite with evidence for every failure. Free to start — no card required.